Cyberattack Targets Three French Plasma Storage Sites, but Blood Products Remain Safe
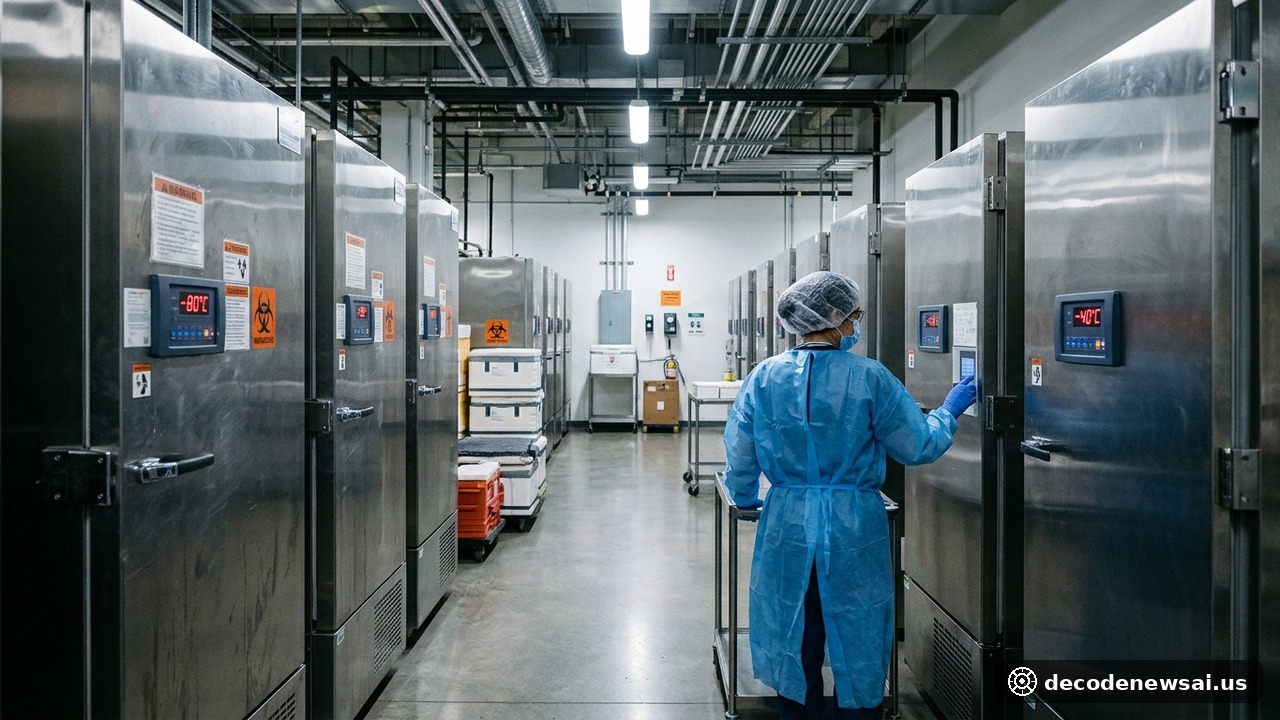
France’s national blood service says a cyberattack altered refrigeration settings at three plasma-storage sites, raising temperatures and defrost thresholds to unusually high levels. The incident, detected on November 2, did not result in lost blood products or identified health consequences, according to the Établissement Français du Sang (EFS). The episode marks a significant expansion of a recent wave of attacks against internet-connected refrigeration systems in Europe: the target was no longer a supermarket’s food inventory, but infrastructure supporting medical supplies.
Remote settings were changed at three sites
EFS said anomalies were detected at three cold-storage locations used to hold plasma. The stored products included plasma intended for transfusions and plasma used in the manufacture of medicines. The attackers sought to raise temperature and defrost thresholds through systems associated with refrigeration equipment. If such settings remain altered, cold-storage rooms can warm beyond the conditions required to preserve sensitive medical products.
The blood service said monitoring and alarm systems detected the changes quickly. Staff intervened, secured the affected equipment and transferred or otherwise protected products stored in the impacted rooms. EFS reported that no blood products or samples were compromised. Blood collection and distribution operations continued without interruption, meaning hospitals did not experience a reported disruption to their supply through this incident.
EFS has not publicly identified the three sites, specified how many refrigeration units were affected, or released a complete technical account of the intrusion. It has emphasized that the blood service itself was not directly targeted. Instead, the incident involved a third-party provider responsible for refrigeration equipment or its management systems.
Coolworld points to a third-party component
Coolworld, a refrigeration-equipment provider, issued a statement on November 4 acknowledging a cybersecurity incident involving remote-monitoring software used in refrigeration systems. The company said the vulnerability described in media reports related to a component supplied by a third party and was outside Coolworld’s direct control. It said only a limited number of its units were affected and that it had responded promptly and was working with customers where necessary.
Coolworld did not identify the affected customers, name the third-party component supplier or provide technical details about the vulnerability. EFS also did not name the service provider in its public statement. French newspaper Le Monde reported that the three affected cold rooms had their temperature and defrost thresholds raised, while the plasma stored there was transferred or secured.
The distinction between a direct attack on EFS and an incident reaching the organization through a supplier matters. Remote maintenance and monitoring can connect equipment at a hospital or blood-storage site to systems operated by outside companies. A weakness in one part of that chain can therefore affect a critical service even when the institution’s own network is not the initial point of compromise.
The incident comes amid wider attacks on refrigeration
The attack follows reports of remotely manipulated refrigeration systems at supermarkets in France and other European countries. Retailers in several countries reported refrigerators or freezers warming after attackers changed settings or interfered with defrost functions, causing food losses. The Record reported that the latest wave had affected businesses in at least 11 European countries, although the full scope and common origin of the incidents remain unclear.
There is no public evidence establishing that the attack on the French blood service and the supermarket incidents were carried out by the same group. Nor have authorities publicly attributed the broader campaign to a particular state, criminal organization or individual. The Guardian reported that European officials were discussing the incidents collectively, while experts have described several possible explanations, including state-backed signaling or activity by an individual actor. Those possibilities remain theories, not confirmed attribution.
French authorities are investigating. EFS said it had strengthened monitoring of its equipment, and the national cybersecurity agency, ANSSI, and the Health Ministry are involved in the follow-up. The investigation is expected to clarify the method of access, the number of potentially affected devices and the timetable for returning impacted installations to normal operation.
A warning about connected medical infrastructure
The incident illustrates how cybersecurity risks can reach medical supply chains through systems that may not look like conventional healthcare IT. Blood-storage facilities depend on refrigeration, temperature monitoring, alarms and maintenance services. When those systems are remotely connected, their configuration and availability become potential targets. An attacker does not need to access patient records or handle blood products directly to threaten the conditions that keep those products usable.
In this case, alarms and staff intervention prevented reported damage. That outcome should not be mistaken for proof that the attempted manipulation was harmless: the attack sought to alter the environment in which plasma was stored, and the consequences could have been serious if the changes had gone unnoticed. At the same time, available evidence does not establish the attackers’ identity, their motive or whether the event was coordinated with other European incidents.
The facts confirmed by EFS are narrower and important: three plasma-storage sites were affected; products were secured or moved; no blood products were lost; and collection and distribution continued. The technical investigation remains open, and any claim about who was responsible would be premature.
Sources
- Reuters: French blood banks hit alongside cyberattack on European supermarkets
- The Guardian: French blood banks hacked in latest cyber-attack on Europe
- The Record: French blood service hit by Europe-wide cyberattacks on refrigeration
- BleepingComputer: Cyberattack disrupts blood storage refrigeration systems in France
- Associated Press / ABC News: Cyberattack hits French blood bank site but no blood products were compromised