Enterprise cybersecurity and data resilience company Rubrik (NYSE: RBRK) officially announced the release of its DevOps Protection Enterprise Edition on Tuesday, November 10, 2026, delivering specialized cyber recovery for Microsoft Azure DevOps and GitHub software development repositories. Unveiled during the company's virtual Cloud Resilience Summit, the native cloud platform integrates identity-driven anomaly detection, attack blast-radius investigation, and surgical asset recovery into a unified operational workflow, enabling software development enterprises to recover corrupted code repositories without enforcing organization-wide code freezes.
Software development environments housing source code, automated pipelines, and infrastructure-as-code scripts have increasingly emerged as critical targets for identity-based adversary compromises. Malicious infiltration into continuous integration and delivery pipelines threatens production workloads across modern digital enterprises.
During a technical keynote delivered at the Cloud Resilience Summit on Tuesday, an executive engineering director for DevOps Protection at Rubrik presented the operational architecture. The executive stated: "Source code repositories and continuous delivery workflows represent an essential corporate attack surface. Surgical recovery isolates and remediates malicious alterations from immutable backups, ensuring enterprise development velocity proceeds without prolonged organizational shutdowns."
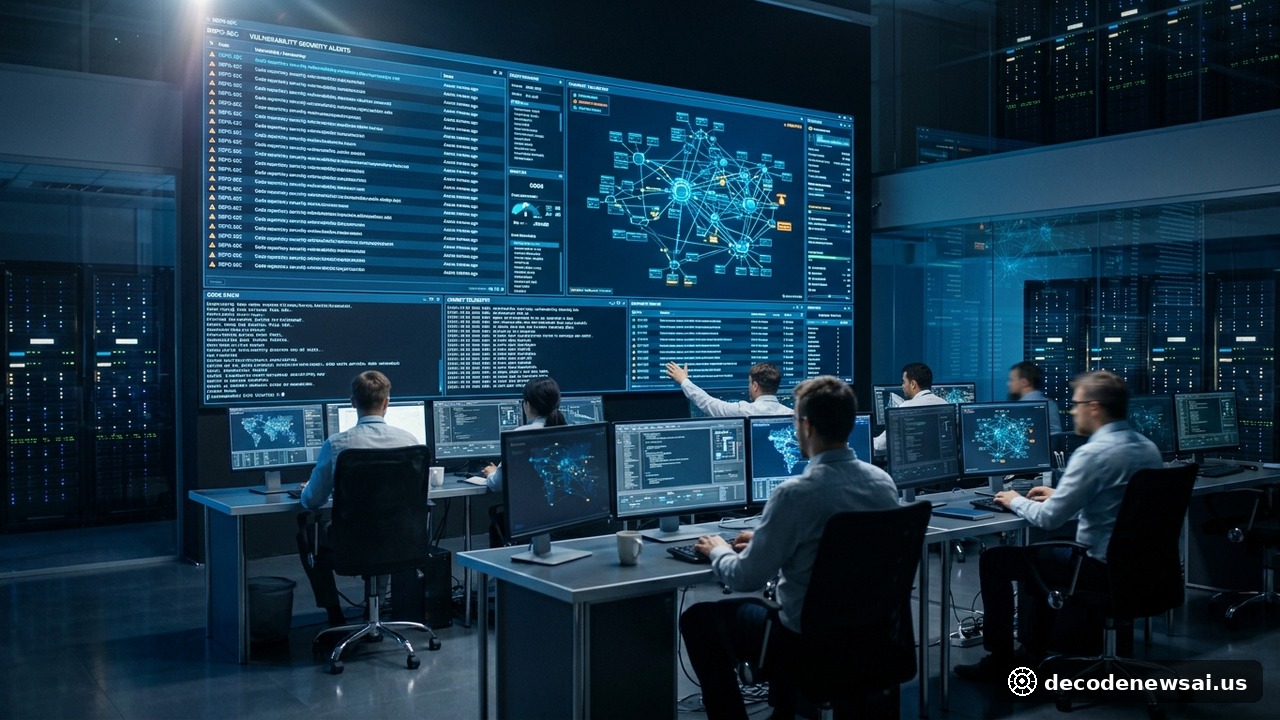
The integrated solution operates directly within Rubrik Security Cloud, addressing the complete incident recovery lifecycle through three coordinated capabilities: Anomaly Detection continuously baselines audit logs across GitHub and Azure DevOps, correlating identity indicators with immutable backup metadata to highlight compromised developer credentials. Blast Radius Investigation constructs an interactive, categorized topological view of affected assets across repositories, commits, pull requests, and administrative settings.
Surgical Recovery restores only altered lines of code and modified workflow configurations using air-gapped, immutable backups, completely preserving legitimate commits authored by authorized engineering staff. The targeted restoration capability eliminates manual system rebuilds and reduces recovery windows from multiple days to under an hour.
Enterprise software analysts and chief information security officers praised the granular recovery paradigm, highlighting that modern application security mandates rigorous disaster recovery protocols embedded directly within development pipelines.
Furthermore, cloud infrastructure security consultants and enterprise compliance auditors observed that integrating automated recovery tooling within source repositories prevents systemic disruptions across critical commercial release schedules. By utilizing air-gapped, write-once backup volumes, enterprise development organizations maintain absolute data fidelity and fulfill statutory cybersecurity mandates. Capital market technology analysts expect cyber resilience platforms to capture sustained enterprise adoption.
In addition, enterprise cloud architects and application security researchers observed that securing developer workflows against identity-driven tampering is vital for safeguarding corporate intellectual property. Because continuous deployment pipelines directly push production code to live infrastructure, detecting unauthorized configuration changes prevents disastrous software supply chain breaches. Information security officers praised granular recovery capabilities for dramatically reducing organizational downtime.
Furthermore, digital forensic investigators highlighted that correlating identity access logs with immutable backup metadata accelerates root-cause analysis during complex cyber incident responses. By eliminating the necessity for complete repository lockouts, enterprise resilience platforms empower software engineering organizations to maintain continuous release momentum while fulfilling strict regulatory cybersecurity compliance mandates.
In conclusion, enterprise cybersecurity executives and cloud software architects emphasized that granular code-level disaster recovery establishes a critical line of defense for modern automated delivery pipelines. Organizations look forward to deploying automated cyber recovery tools to ensure uninterrupted software engineering operations.
Moreover, software development lifecycle auditors and cloud compliance directors emphasized that automated anomaly detection within continuous delivery pipelines prevents unauthorized credential exploitation. Granular recovery workflows enable engineering teams to remediate targeted code tampering rapidly without interrupting overarching commercial deployment deadlines. Chief information security officers and enterprise software engineering teams look forward to deploying automated cyber recovery tools across critical development environments. Application developers and information security leaders look forward to continuous innovations in automated cyber resilience and agile software disaster recovery.